Keep data inside
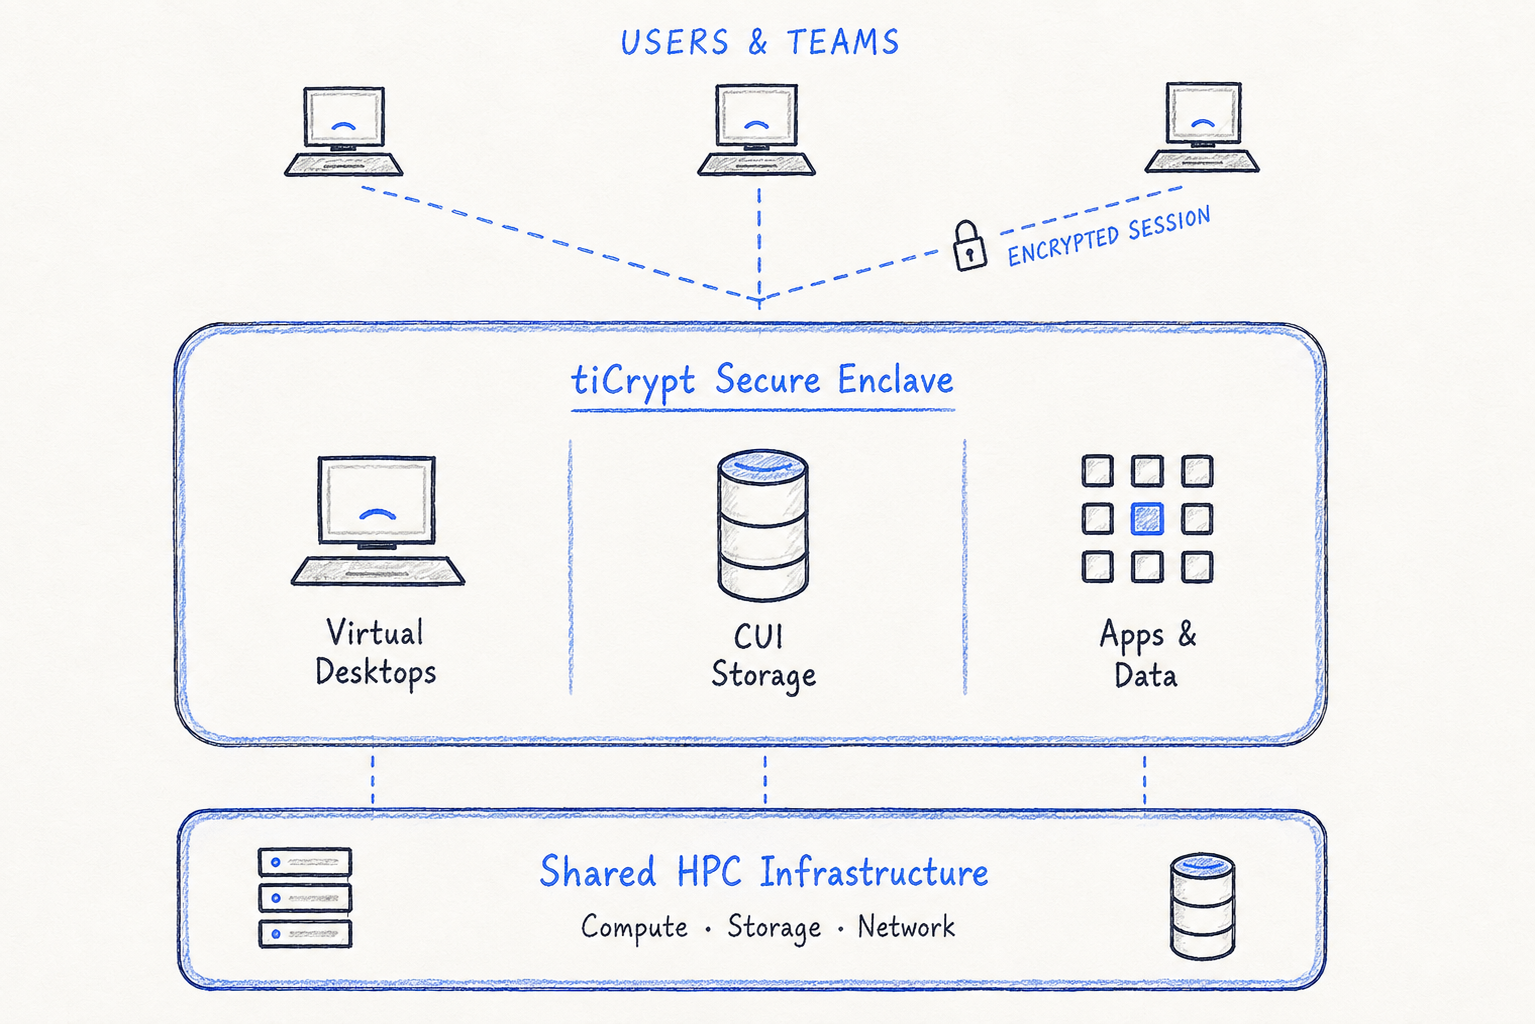
Sensitive data remains inside the secure environment - not on user endpoints.
Protect regulated data. Isolate every project.
Share the infrastructure you already own.
Built by Tera Insights · Proven at the University of Florida
Sensitive data remains inside the secure environment - not on user endpoints.
Each project has its own users, keys, policies, and access boundaries.
Use common HPC, GPU, storage, and applications without sharing project trust.
Access the tools and environments you need - your way.
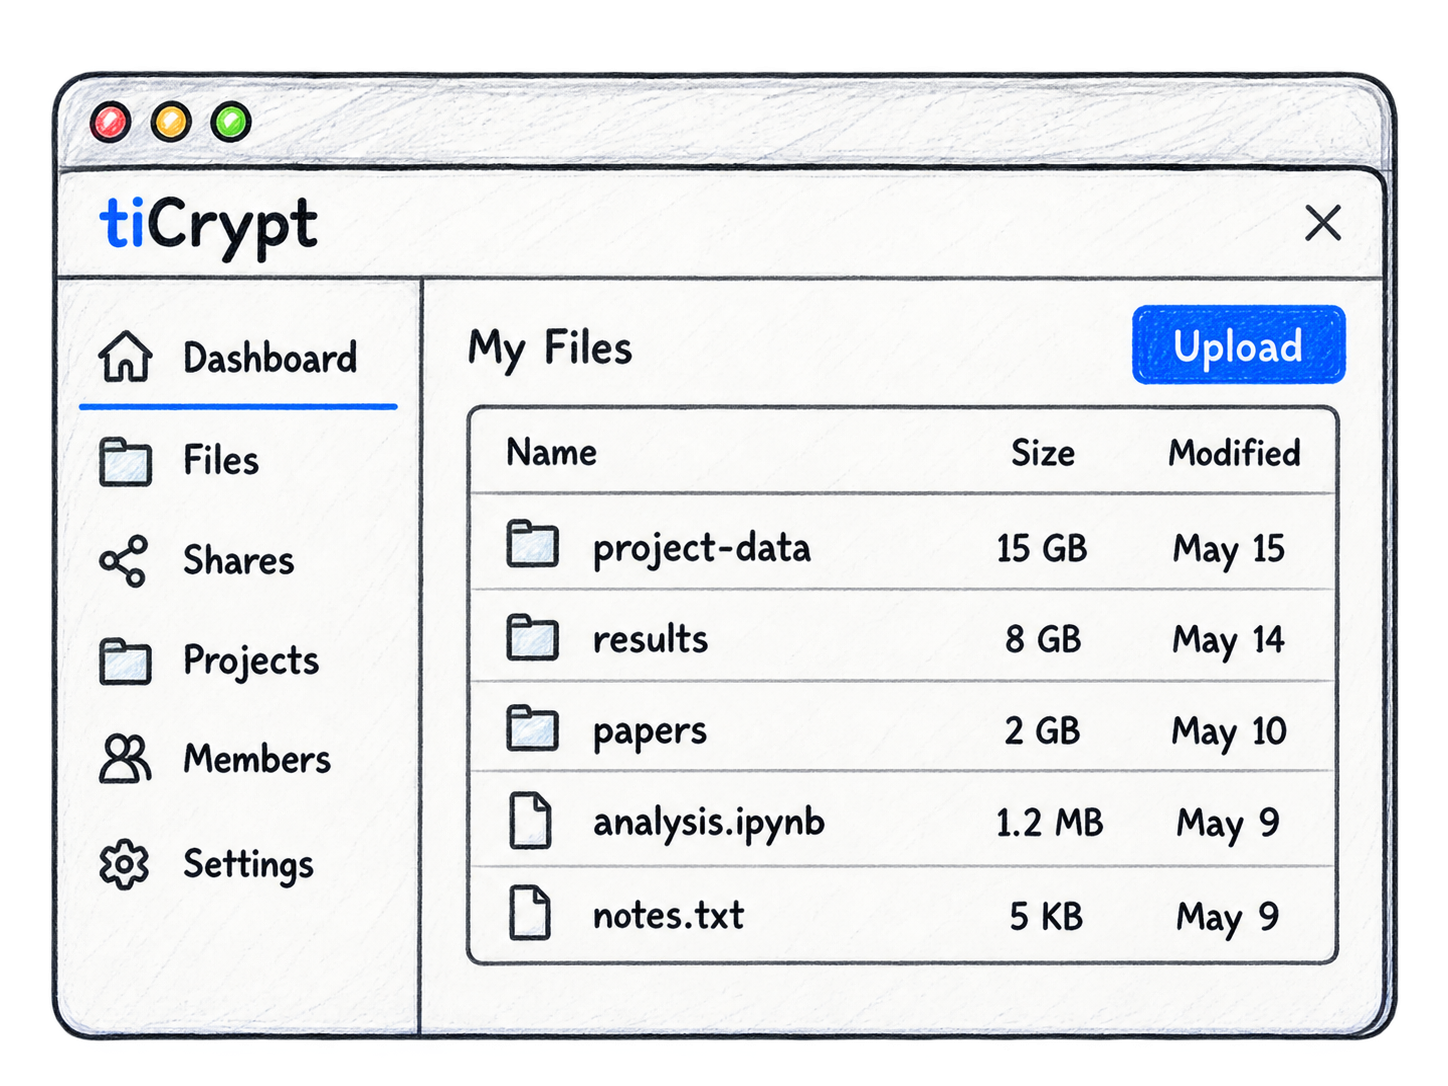
Use the tiCrypt web portal to upload files, share securely, and manage your resources.
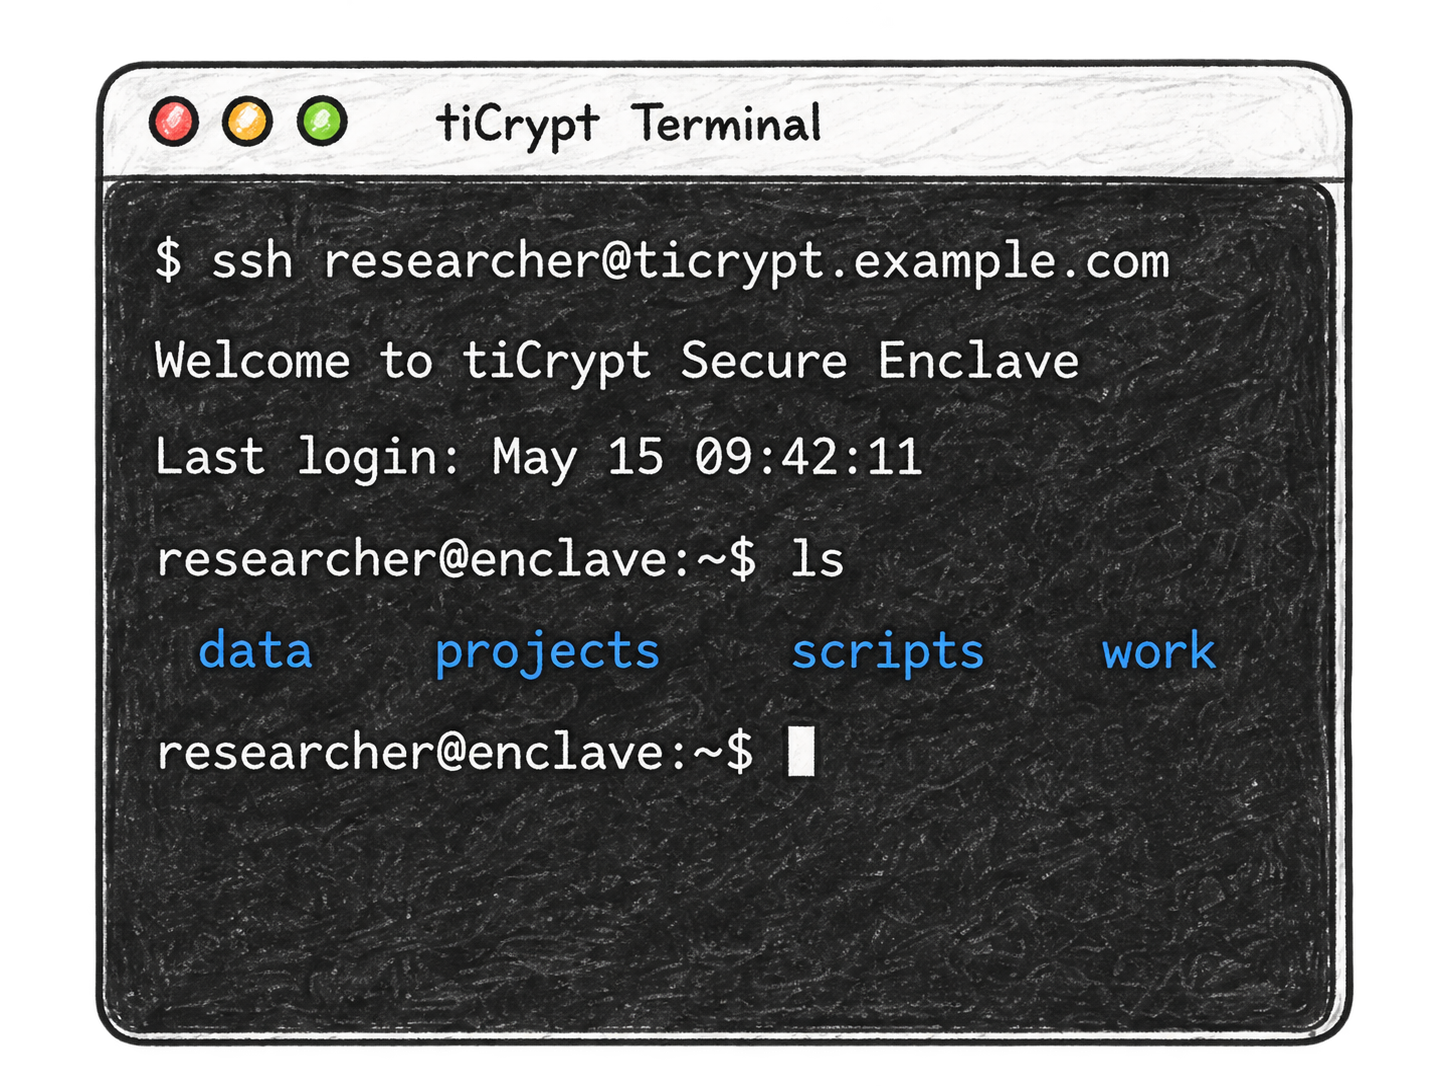
Use your terminal to access tiCrypt environments and HPC workloads.
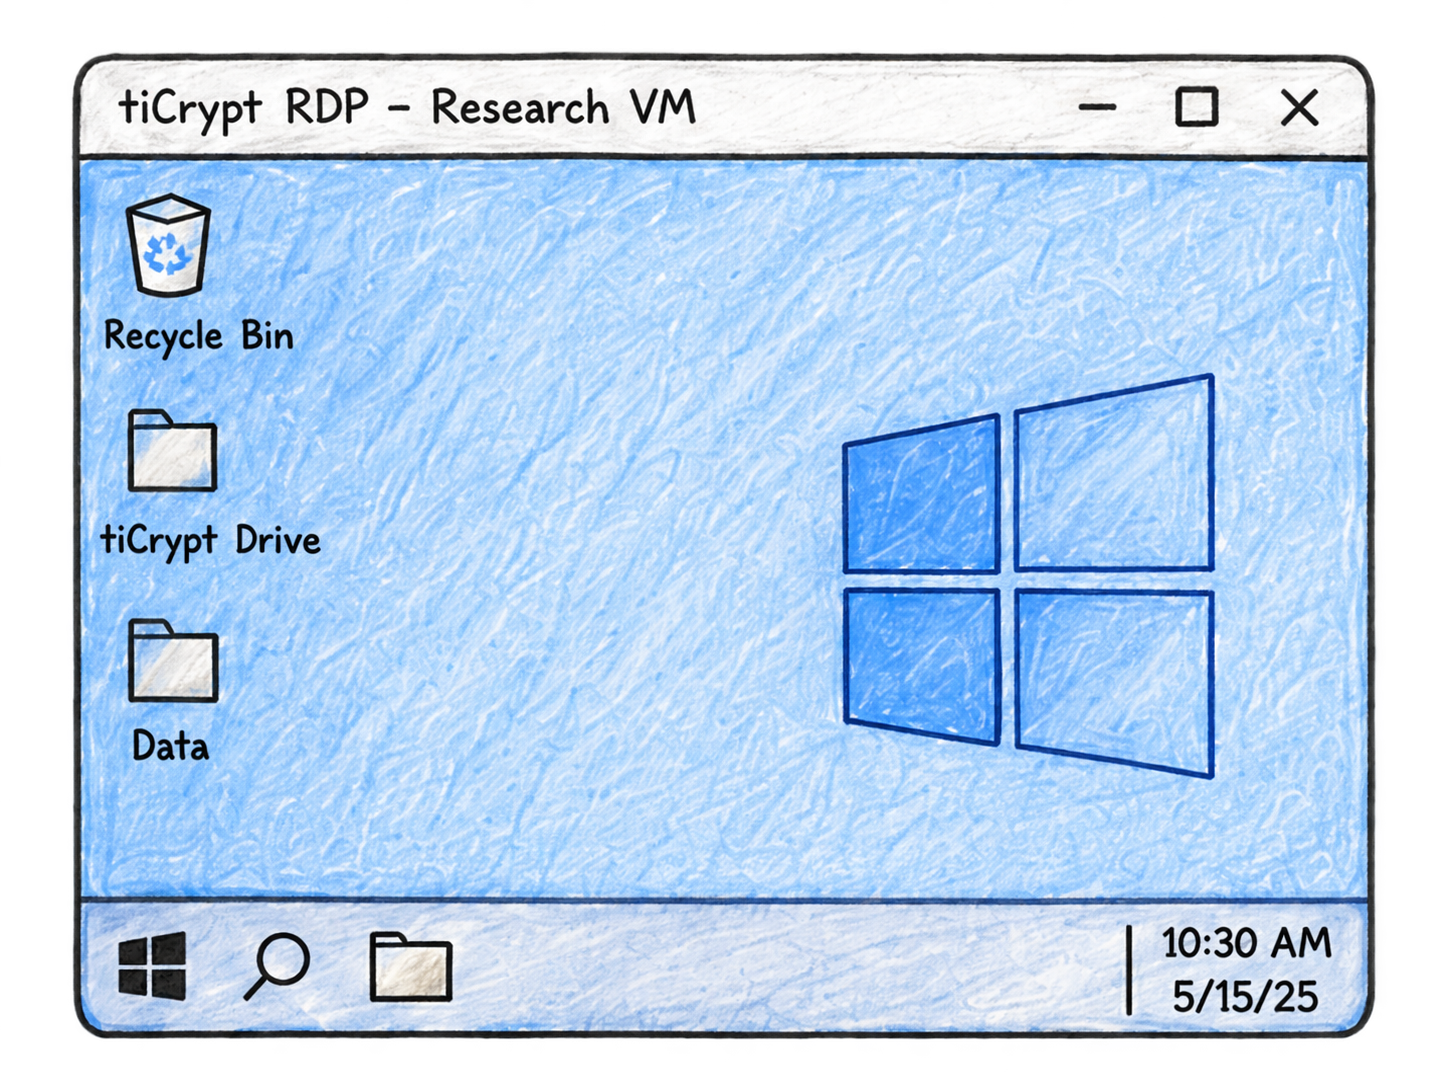
Use RDP to connect to Windows virtual desktops for a familiar, full-featured experience.
Strong cryptography isolates projects while enabling efficient use of shared infrastructure.
See how it works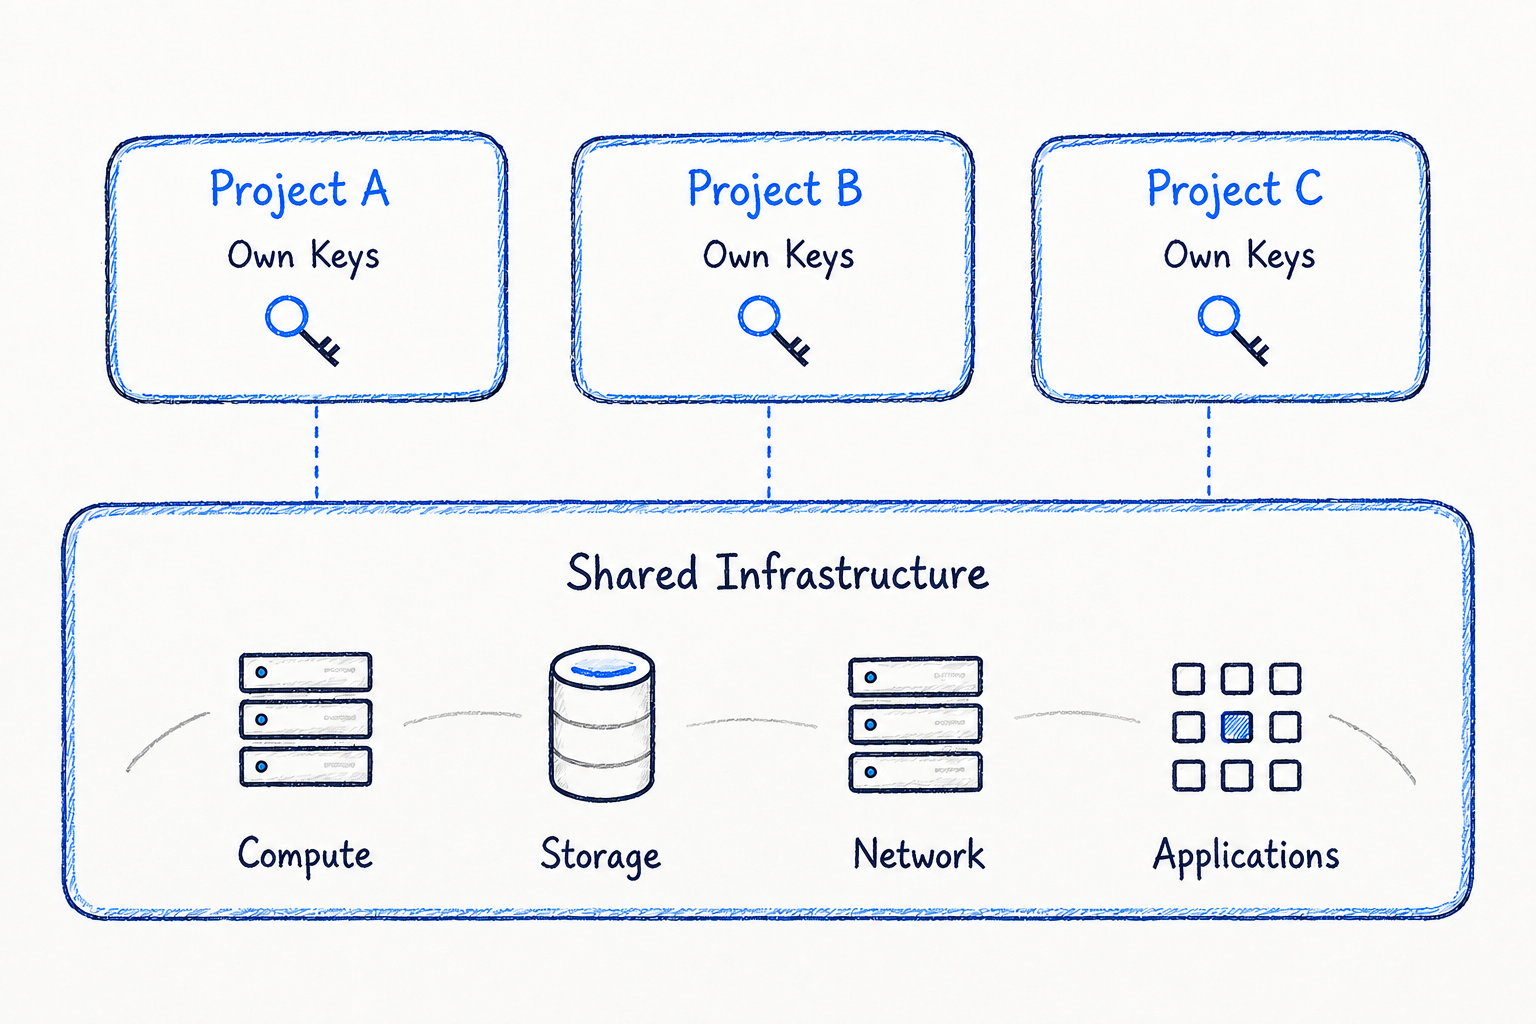
Maximum Utilization. No Shared Trust.
Linux · Windows · GPU · HPC · SLURM
Secure shared access to HPC resources without separate clusters for every project or program.
Run HPC jobs without moving sensitive data outside the encrypted environment.
Share CPU and GPU compute while maintaining cryptographic project isolation.
Split-instance SLURM orchestration separates scheduling from execution inside secure project environments.
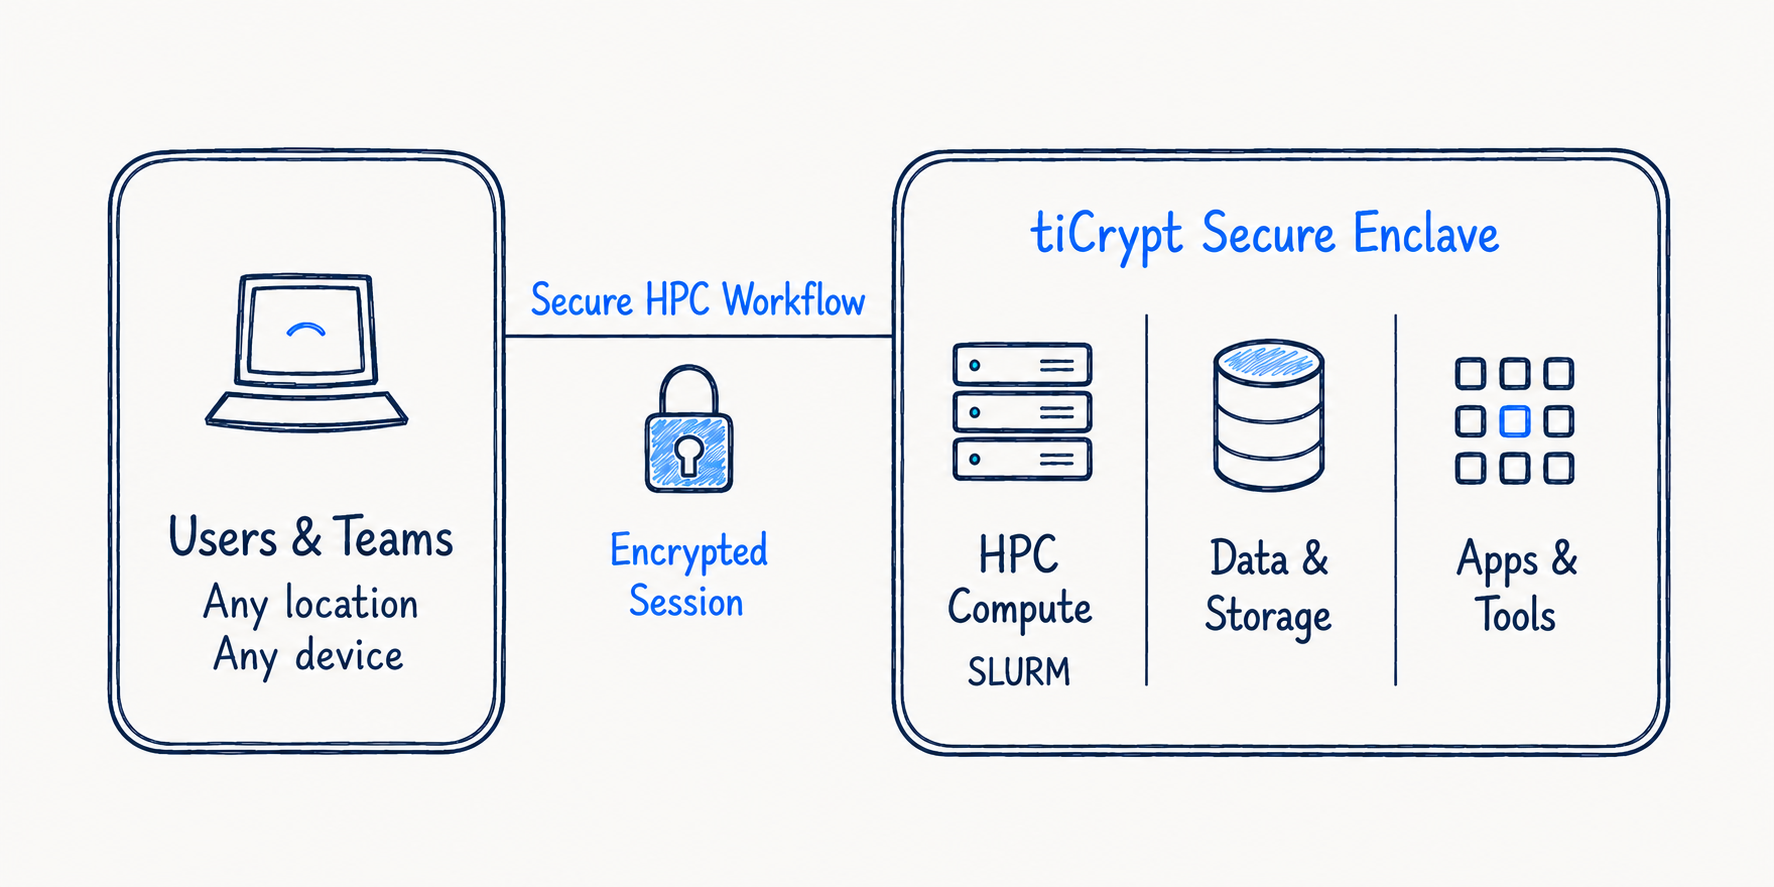
Linux · Windows · CPU · GPU · Clustered · Batch · SLURM
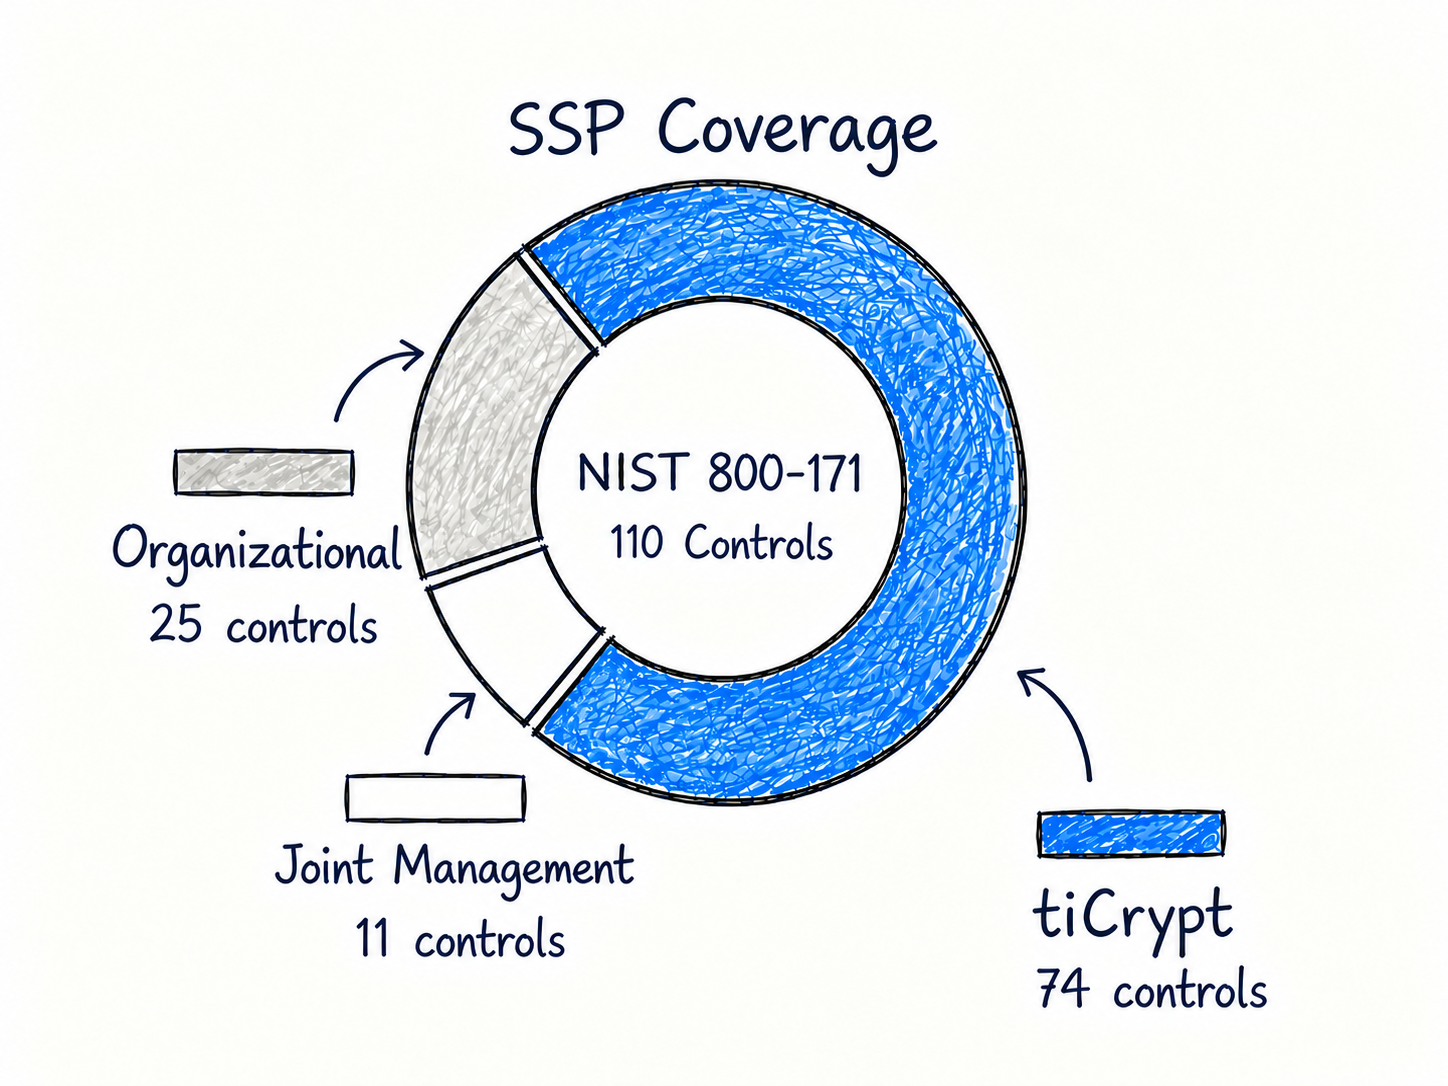
Enforced by the tiCrypt platform.
Reducing risk and audit effort.
With NIST 800-171 Rev. 3 and CMMC Level 2.
Tracks activity across the environment.
Delegates project management without giving up infrastructure control.
SSO · Multi-organization support · Role-based delegation · Central audit trail
Data and VM storage encrypted with AES-256.
Per-user cryptographic identity and key protection.
Cryptographic operations use a FIPS 140-3 validated module.
Private keys never reside on tiCrypt infrastructure.
Built to operate at scale: Centralized audit logging · Role-based delegation · SSO · Multi-organization support
Linux: LUKS · Windows: BitLocker · PKI/digital-signature authentication
Explore the security architectureUse the infrastructure you already own. Run unlimited secure projects through a single security stack.
See full comparisonOur independent security review and penetration test of tiCrypt revealed an exceptionally strong, defense-in-depth architecture aligned with NIST 800-171. The platform incorporates non-default security design choices not commonly encountered in comparable systems. We were particularly impressed by the overall security architecture and the team’s responsiveness.”
Our tiCrypt environment has significantly improved collaboration between the college and hospital by providing researchers from both organizations a shared space to work with highly sensitive data. We have enjoyed watching the platform mature and continually improve. As we find new use cases, Tera Insights has been great to help us find solutions.”
We have been working with Tera Insights for about a decade on building a computing environment for working with restricted data that is flexible, highly secure, and straightforward to manage. With constant feedback from researchers, the environment has matured to meet the demands of very complex workflows.”
After completing our penetration test of the tiCrypt LASER environment, we came away genuinely impressed. The platform reflects a layered, thoughtful security architecture built with compliance and protection at its core. For organizations working with sensitive data, tiCrypt is an exemplary model.”
See how tiCrypt can fit into your existing research and HPC infrastructure.